Supabase RLS
Supabase RLS for Team and Organization Apps: A Practical Starting Point
A starting point for Supabase RLS policies in team, organization, workspace, and shared-record apps.
Supabase RLSSupabase Keys
Is It Safe to Expose Your Supabase Anon Key?
How to reason about visible Supabase anon keys, RLS policies, and what actually protects user data.
Supabase RLS
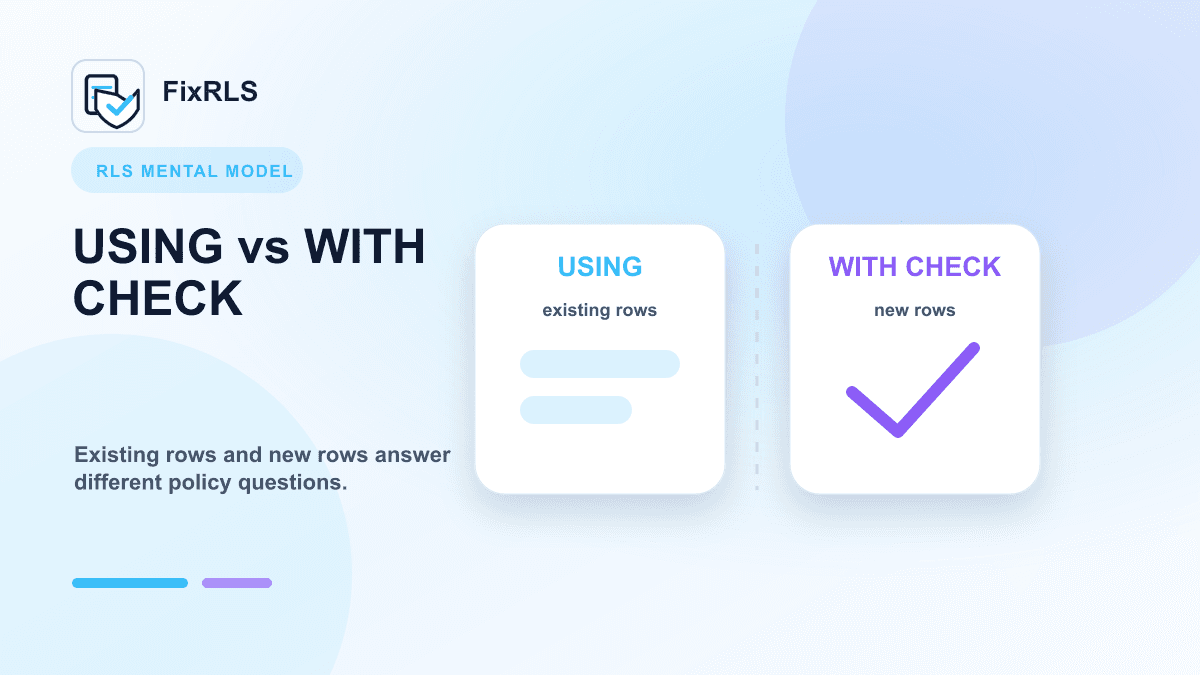
Supabase RLS: `USING` vs `WITH CHECK` Explained with Examples
Clear examples showing how USING and WITH CHECK answer different Supabase RLS policy questions.
Supabase RLS
Supabase RLS INSERT Policies: Why `WITH CHECK` Matters
Why Supabase INSERT policies need WITH CHECK and how that differs from USING for existing rows.
Supabase RLS
How I Fixed "new row violates row-level security policy" in Supabase
Fix Supabase new row violates row-level security policy errors: insert and update variants, auth.uid() issues, a worked example, and proof tests.